District 01 · Digital Outlaws

Offensive security · White hat

Find the breachbefore the outlaw does.

Penetration testing and ethical hacking under signed authorization. Hackerman 253, our white-hat sheriff, widens coverage with AI agents. An engineer validates every finding.

  • 17 assessment lines
  • Written authorization, always
  • Every finding human-validated

The threat

Attackers already use AI. Get there first.

The worst part is finding out late, from a customer or the press.

Probe station

Order an exposure probe of your company

No cost and 100% passive. Our team reviews what anyone can see about your company from the internet and sends you the findings with a quote.

Station SU-253Online
  1. Identify yourself
  2. Authorize
  3. Contact details
  4. Order sent
Target
Unassigned
Authorization
Pending

Identify yourself with your work email

The domain to probe is taken from your email. That way nobody can order a probe of a company that isn't theirs.

The probe is passive: it does not access your systems or test vulnerabilities, and it does not replace a penetration test. It can only be ordered for the domain of the verified email.

What we assess

Your entire attack surface

Tap a zone on the map to see what we test there.

01

Web & portals

Access, sessions and OWASP Top 10 flaws across your portals and sites.

See all 17 assessment lines

Surface and infrastructure

  1. Reconnaissance and external attack surface
  2. Infrastructure and network vulnerability scanning
  3. External penetration testing
  4. Internal penetration testing

Applications

  1. Web application security (OWASP Top 10)
  2. API security
  3. Mobile applications

Identity and encryption

  1. TLS/SSL configuration and encryption
  2. Authentication, authorization and tenant isolation

Cloud and data

  1. Cloud and containers / Kubernetes
  2. Databases

Code and supply chain

  1. Source code review (SAST) and exposed secrets
  2. Supply chain / dependencies

Advanced

  1. Assessment aligned with PCI DSS v4.0.1 and ISO/IEC 27001:2022 (not a certification)
  2. AI agent security
  3. Red team / blind assessment
  4. Revalidation (retest)

Methodologies: OWASP, PTES and NIST SP 800-115. Severity scored with CVSS.

Hackerman 253

Machine speed. Human judgment.

Hackerman 253 is our virtual specialist in ethical offensive security. People lead it and agents speed it up: nothing reaches your report without human validation.

  • The 3X method

    Three analysis engines cross-checked, plus human review. Real findings only.

  • You decide how much the attacker knows

    Black, gray or white box, depending on what you want to put to the test.

  • Criticals, immediately

    If we find something serious, you hear about it right away, not in the final report.
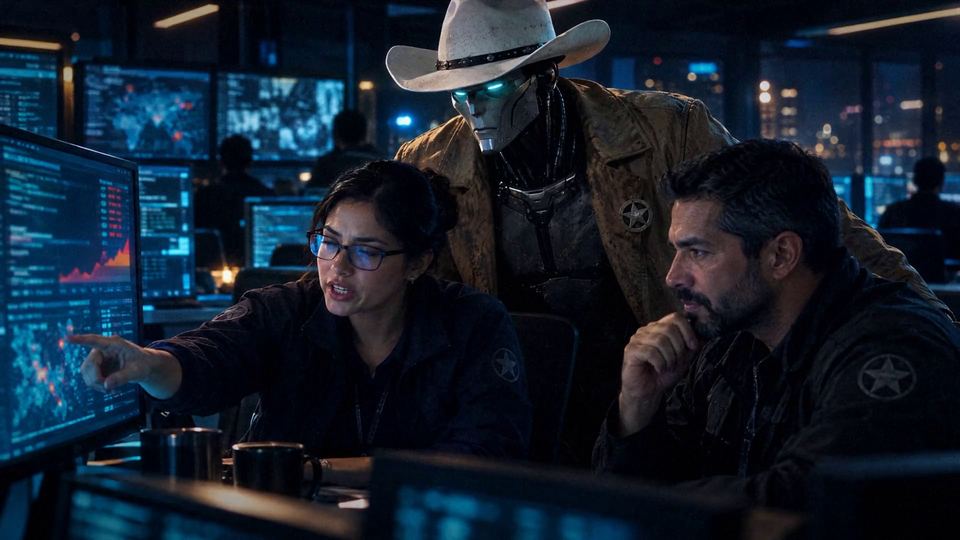
Hackerman 253 with two engineers reviewing findings on screen
  • Black box

    No prior knowledge, like an outsider.

  • Gray box

    With a user account or partial access.

  • White box

    With documentation and code.

Rules of engagement

Same techniques as an attacker. Opposite purpose.

Before we touch a single system, we agree in writing on:

  1. Written authorization from the owner (form SU-EH-FRM-001).
  2. In-scope and excluded assets, one by one.
  3. Agreed execution windows.
  4. A stop keyword: say it and we halt.
  5. Declared source IPs for your allow list.
  6. Advance notice to your SOC or MSSP.
  7. Credentials only through a secure channel.
  8. Encrypted evidence, retained 90 days and then destroyed.
  9. We never store PAN or CVV.

What you get

Two reports. Findings only.

PDF

Executive report

For leadership and the board: risk and business impact in plain language.

PDF

Technical report

For your team: every finding with a CVSS severity and reproducible evidence.

Self-assessment

How does your security posture look?

Ten questions, two minutes. You get a reading by area and where we would start.

Question 1 of 10Visibility

Do you keep an up-to-date inventory of what your company exposes to the internet (domains, APIs, apps, cloud)?

You can answer with keys 1 to 4.

For orientation only: it is based solely on your answers. We scan nothing and this does not replace a penetration test. We never ask for passwords or sensitive data.

Sample report

See exactly what you'll receive

Both reports from a fictitious assessment (NovaPay Financial), exactly as we deliver them. We send them by email. The sample is in Spanish.

  • Executive report (PDF)
  • Technical report with CVSS and evidence (PDF)
  • Links valid for 7 days

How we work

Five phases, no surprises

  1. Request and scope

    You sign form SU-EH-FRM-001.

  2. Planning

    Windows, contacts, IPs and stop procedure.

  3. Execution

    With logs and evidence recorded.

  4. Results report

    Findings ranked by CVSS.

  5. Close-out

    Secure delivery, agreed retention and evidence destruction.

Next step

Request your security assessment

Together we define the scope, the test windows and what's off-limits. Nothing is tested without your written authorization.

With country code, e.g. +1 305 555 0100